Moving the SOC closer to autonomy with powerful AI agents, expanded protection for enterprise AI, and blazing-fast search
Security operations is on the verge of its biggest transformation yet. As frontier AI accelerates attacks and expands what adversaries can automate, the SOC must evolve beyond AI assistance toward greater autonomy. That means AI agents that can understand the enterprise, collaborate with analysts, and handle increasingly complex investigations from start to finish.
The launch of Cortex XSIAM 4.0 delivers on this vision. This milestone release equips SOCs with autonomous, context-driven AI agents that collaborate seamlessly with human analysts to accelerate investigations, streamline response, and defend the enterprise against AI-fueled threats.
AI Agents Become Part of Your Team
AI agents are moving from the sidelines into the heart of security operations. With Cortex XSIAM 4.0, they bring your organization's collective knowledge into every investigation and work shoulder to shoulder with analysts, harnessing the latest frontier AI models. Armed with a deeper understanding of your environment, agents can take on more complex work and play a greater role in defending the enterprise. These features are also available in the Cortex AgentiX standalone platform.
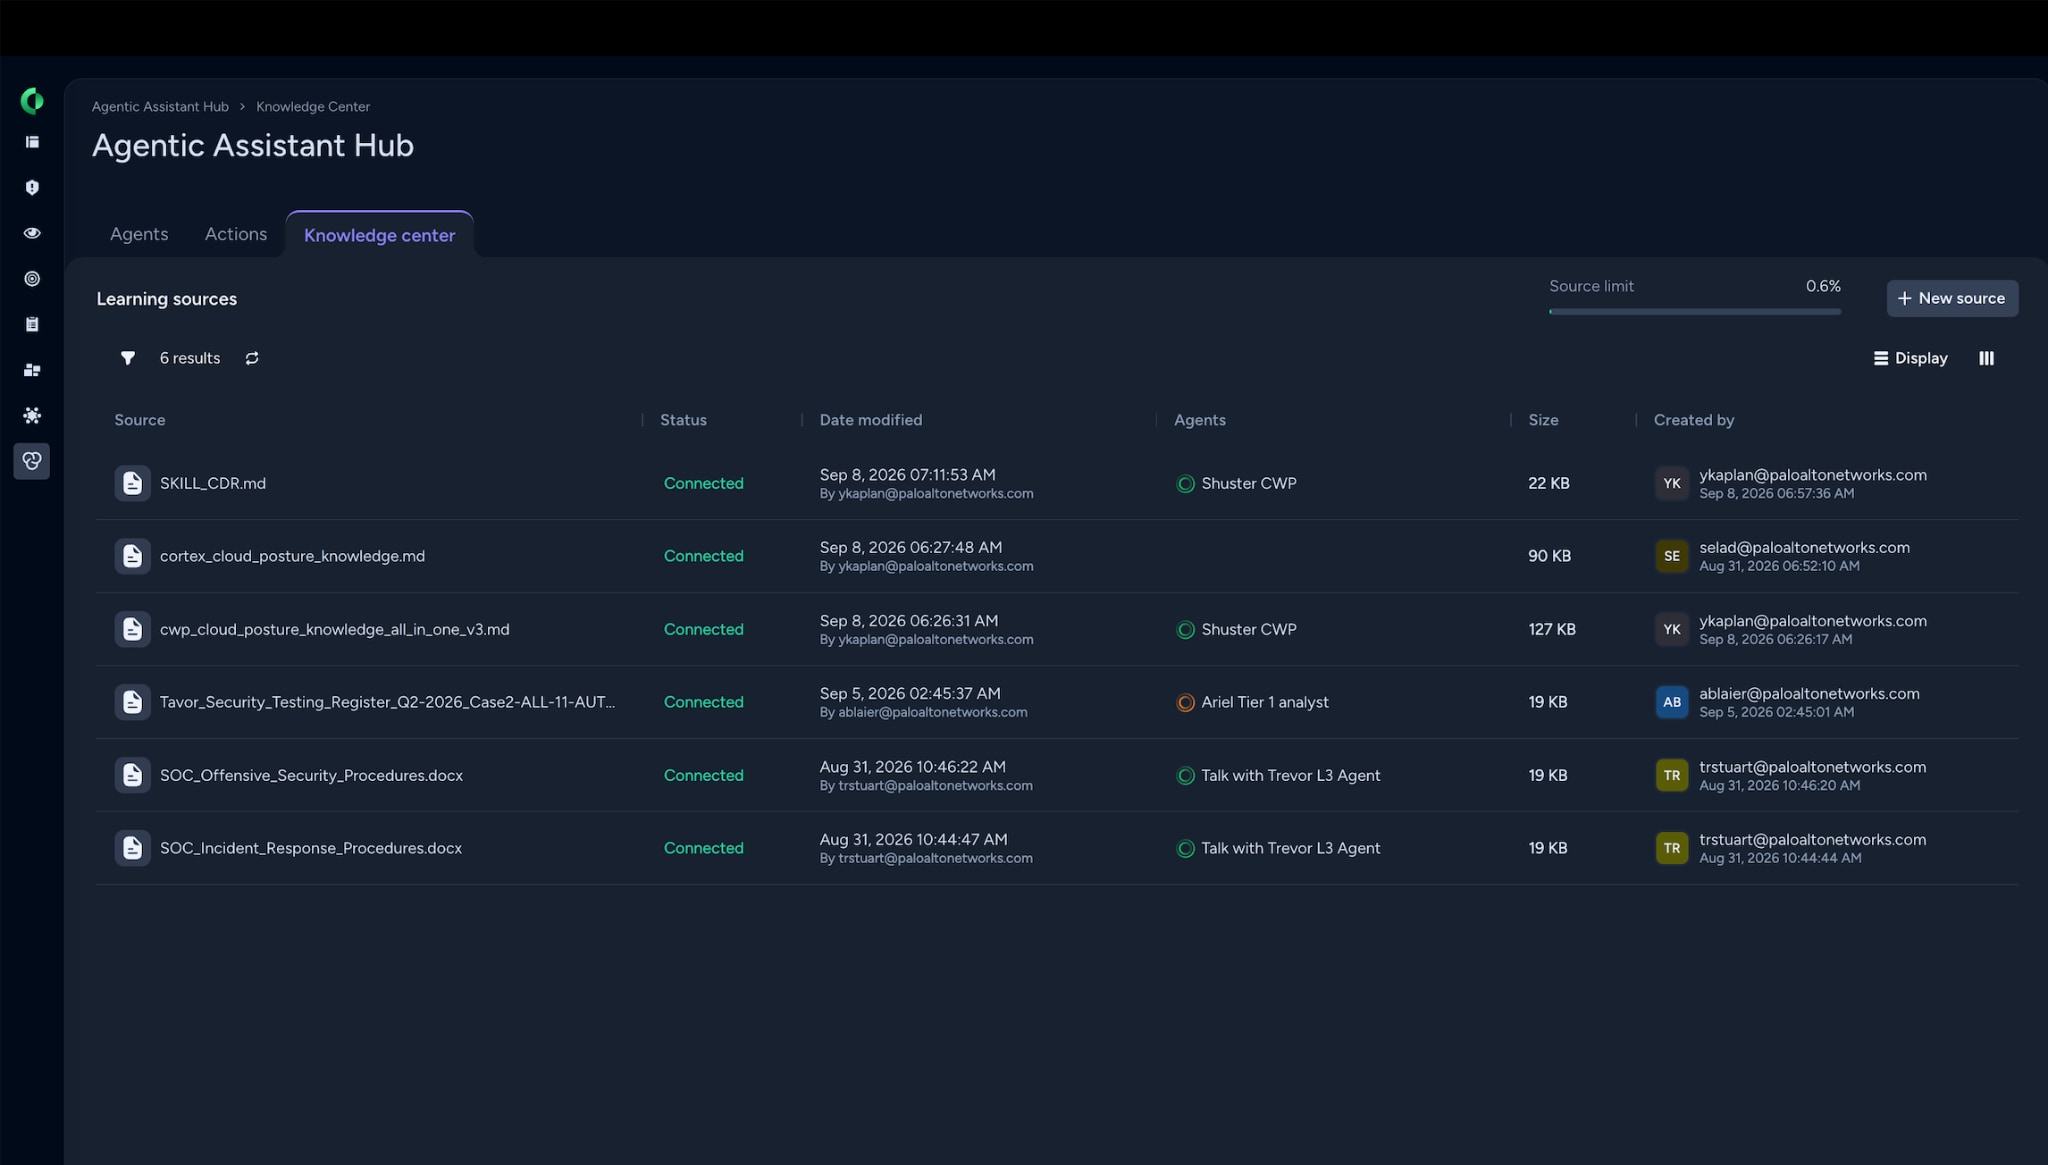
- Agents with Enterprise Knowledge: Give AI agents access to the knowledge your security team has built over years, from Google Drive, Confluence, and SharePoint to internal standard operating procedures (SOPs). Agents bring this institutional knowledge into investigations, using your organization's policies, processes, and expertise to inform their decisions and actions. Agents are smarter but still grounded by the enterprise guardrails, native access controls, and approval gates you’ve defined.
- Agents as Collaborators: Make agents active participants in investigations, working directly alongside your team on cases. Analysts can delegate complex tasks, review findings, and track each agent's contributions. Activity logs and investigation histories stay with the case, preserving valuable context across analyst handoffs. It’s like having additional team members that can be called upon to help resolve cases.
- Frontier AI, Now Globally Available: Put the reasoning power of frontier AI models to work in SOCs around the world. Cortex XSIAM customers can now tap into these advanced models globally, bringing more sophisticated reasoning to investigations and automation. Customers outside the US and EU can remain on local models or complete a permanent, one-time opt-in to US or EU inference hubs.
- Prioritized Playbook Execution: Ensure your most critical threats are addressed first by assigning playbook execution priorities with automation rules. Your team can fast-track playbooks so urgent workflows move to the front of the queue, even during spikes in activity.
Securing a World Where AI Is Everywhere
AI is moving into every corner of the enterprise, writing code, powering applications, connecting to sensitive data, and increasingly making decisions on its own. As adoption accelerates, a new attack surface is taking shape across agents, models, applications, and the systems they touch. The SOC now has a new landscape to defend.
- Agentic Endpoint Security: As AI agents become part of everyday business operations, Cortex XDR extends visibility and protection to the endpoints where they operate. The Cortex XDR sensor discovers AI agents, models, MCP servers, and extensions, helping security teams identify emerging risks and defend against AI-driven attacks.
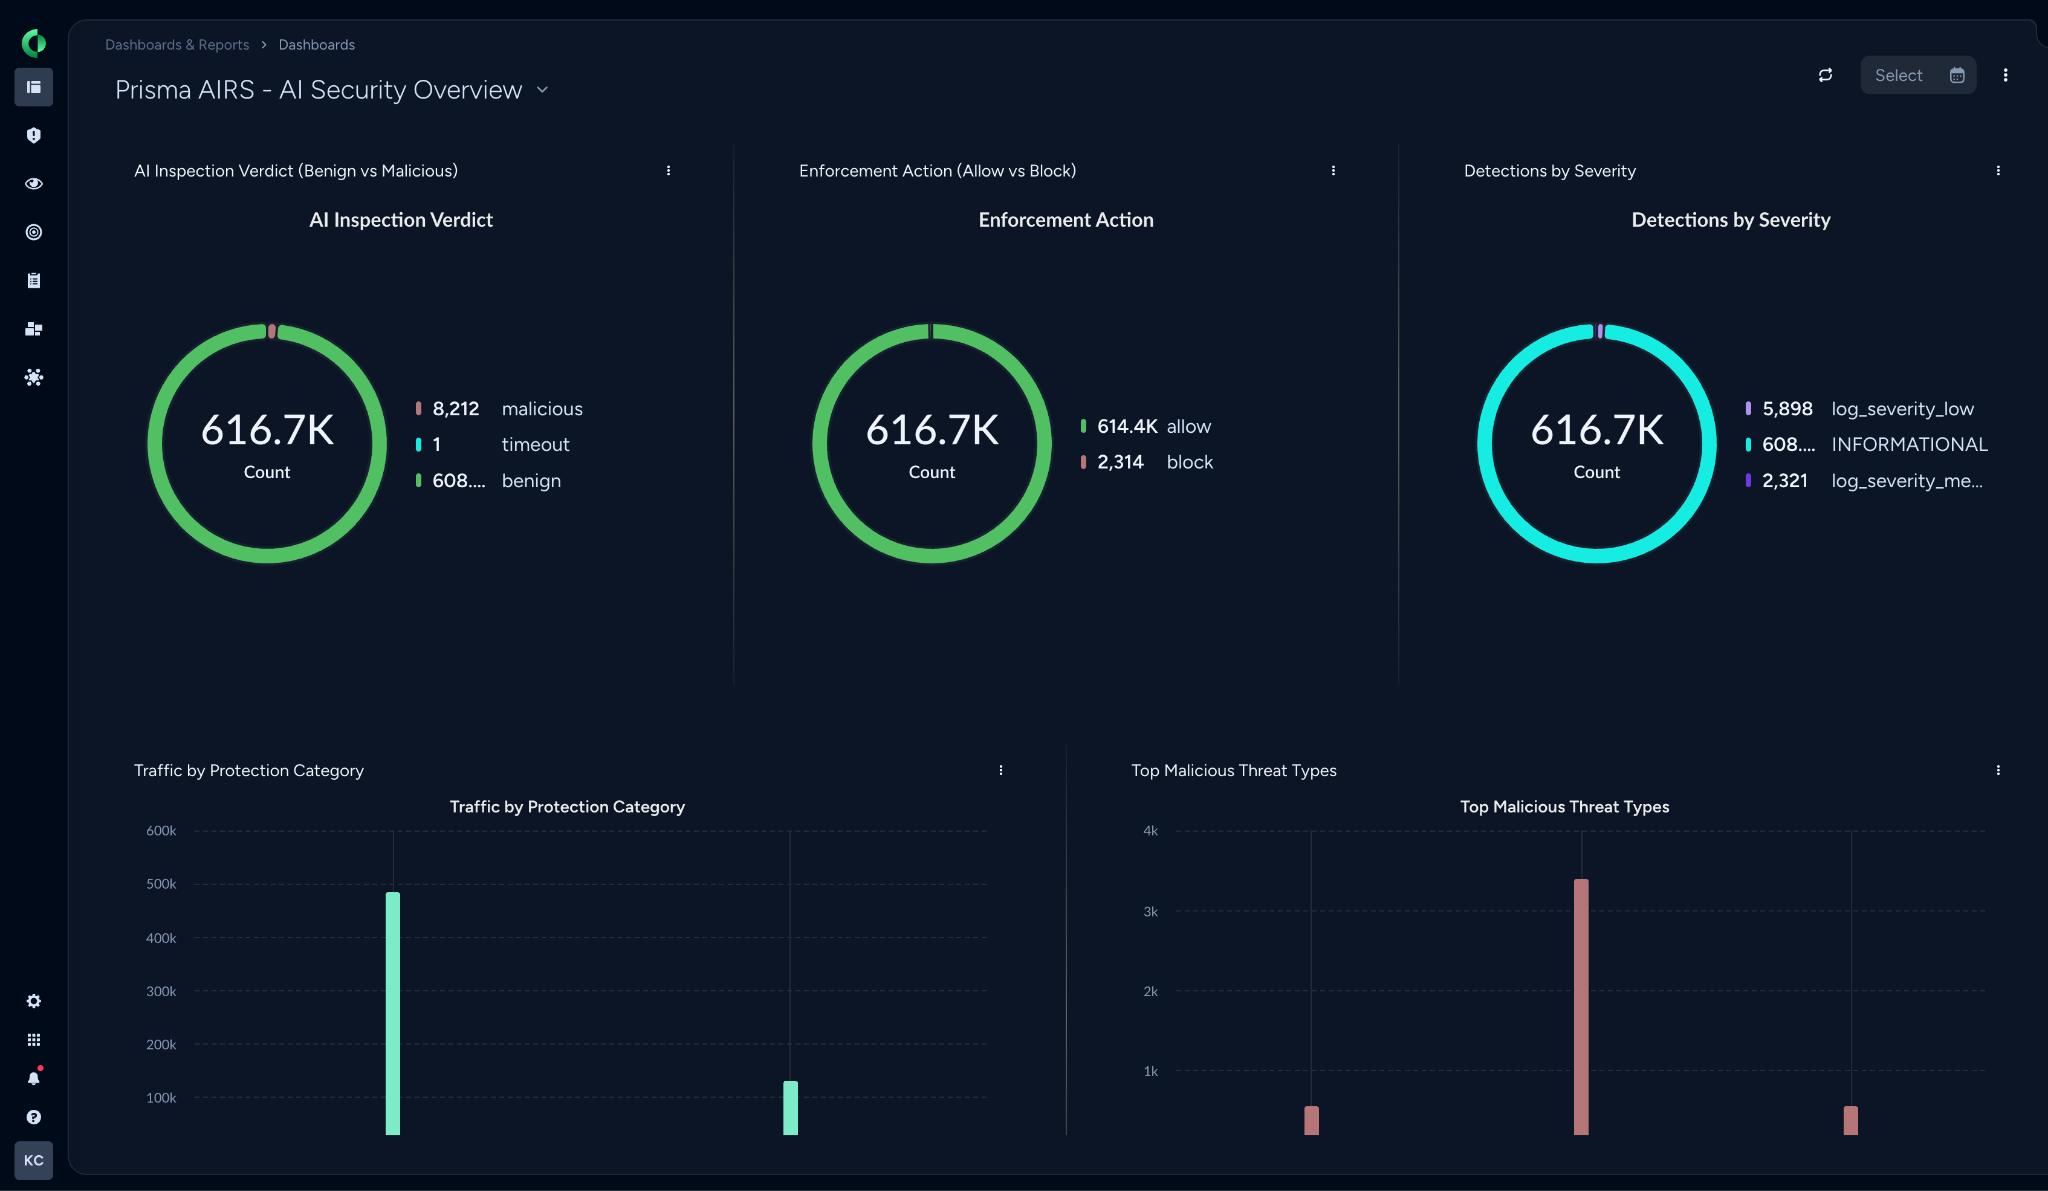
- Prisma AIRS Integration: Cortex XSIAM 4.0 brings Prisma AIRS telemetry into the SOC, connecting threats targeting enterprise AI applications with activity across the broader environment. Analysts can search, detect, investigate, and respond to AI-related threats alongside other security incidents, gaining a more complete picture of attacks that span traditional infrastructure and emerging AI systems.
Taming the Growing Flood of Security Data
Security data is growing at a staggering pace. IDC estimates telemetry volumes are increasing 29% annually, putting mounting pressure on SOC budgets and infrastructure. As the flood of data accelerates, security teams need greater control over what they ingest, faster access to what matters, and the flexibility to investigate data wherever it lives. Cortex XSIAM 4.0 introduces powerful new capabilities to help security teams stay ahead of the curve.
- Data Model Acceleration: Accelerate threat detection and investigations by processing data model rules as telemetry arrives. Cortex XSIAM 4.0 transforms incoming data into standardized XDM fields at ingestion, dramatically improving query performance while preserving the original raw data for deeper investigation.
- Advanced Data Filtering: Take control of ingestion costs at the source. Filter out low-value telemetry early in the data pipeline, using granular XQL-based rules to determine exactly what gets ingested into Cortex XSIAM. Keep the data that matters while reducing unnecessary storage and processing costs.
- Federated Search: Search security data across AWS, Google Cloud, and Azure directly from Cortex XSIAM using XQL, without ingesting or storing it in the platform. Flexible schema editing makes it easier to adapt datasets as your environment evolves, giving analysts access to more data without the added ingestion costs.
Move Faster From Exposure to Protection
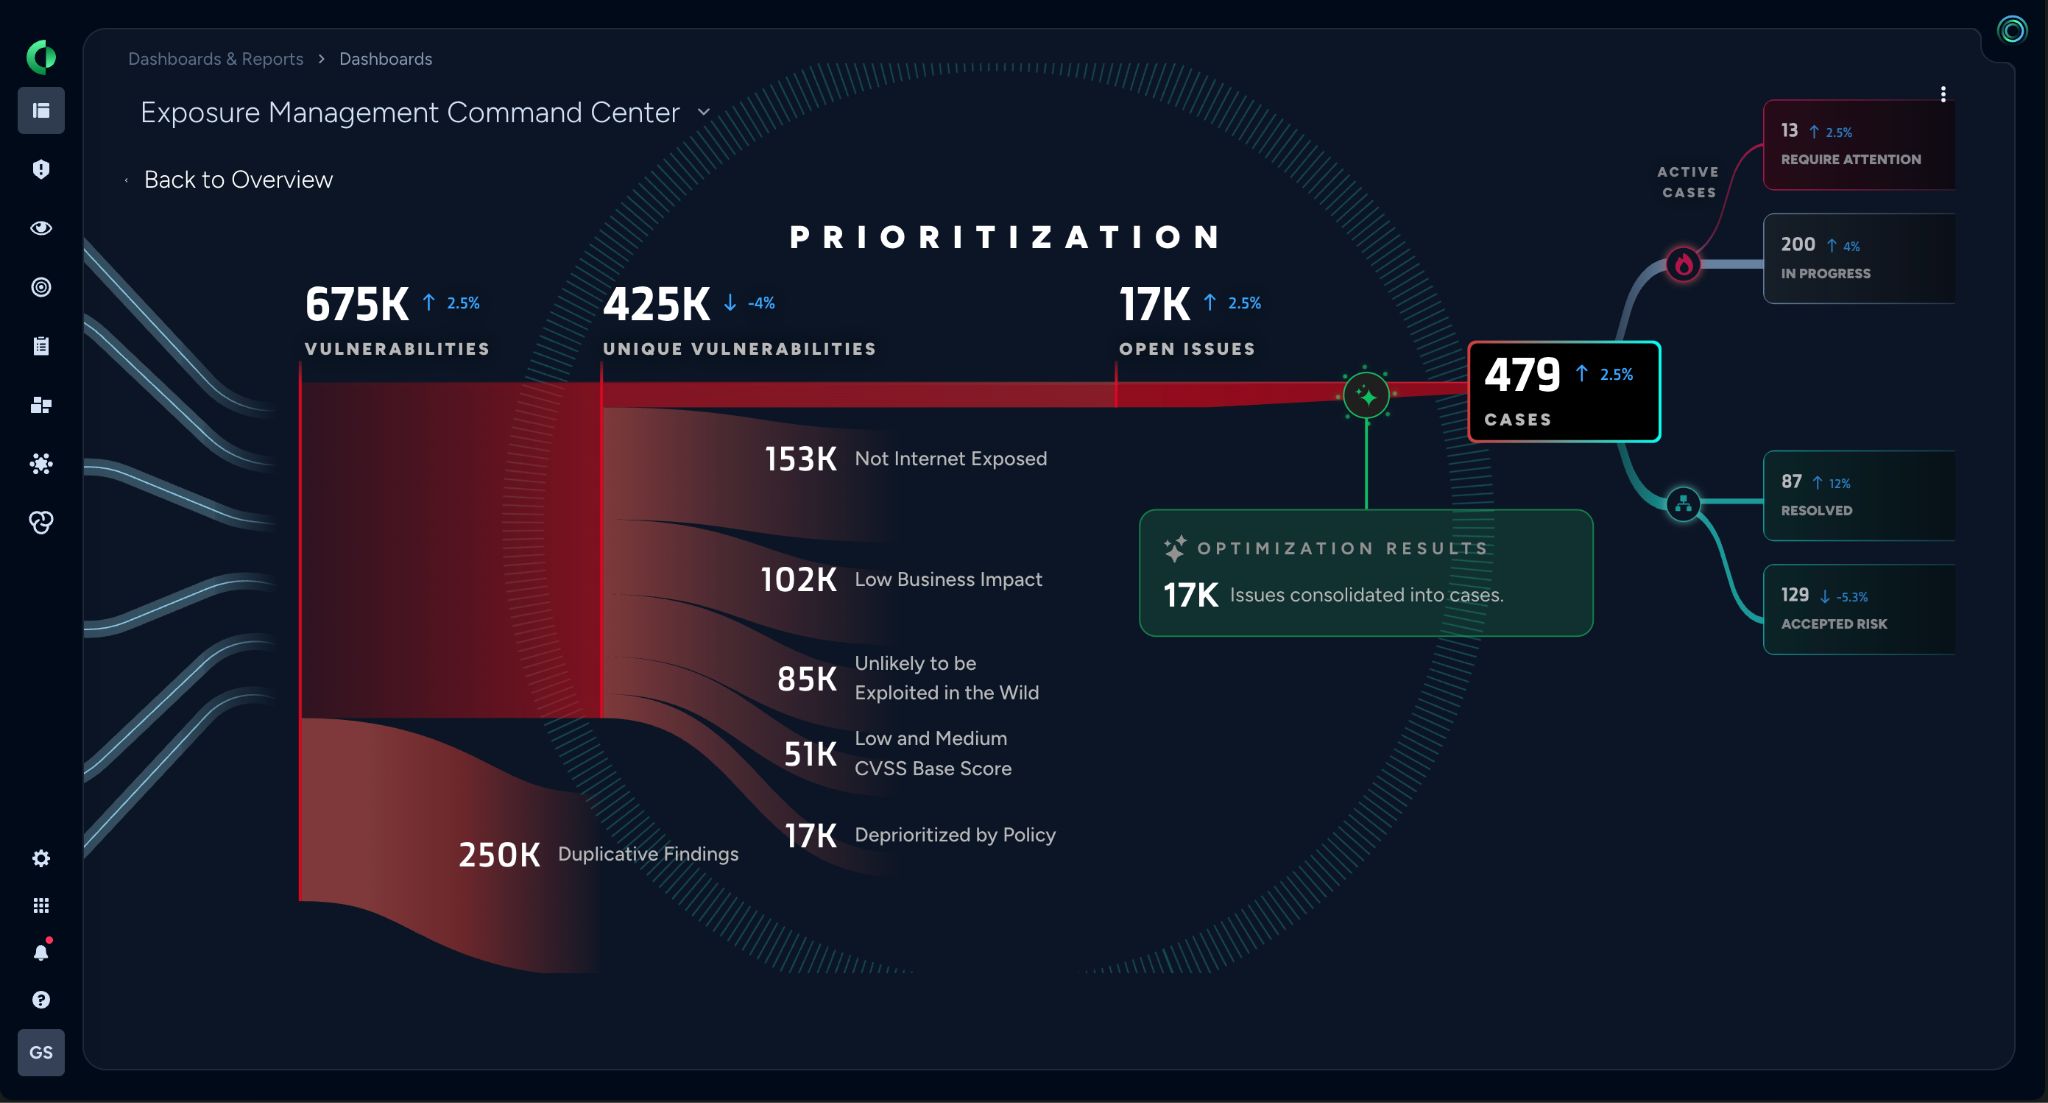
Finding vulnerabilities is only half the battle. Cortex Exposure Management helps security teams focus on the risks that matter, strengthen protection across their environment, and accelerate remediation with new capabilities in Cortex XSIAM 4.0.
- XDR Virtual Patching: Protect vulnerable applications when traditional patching isn't feasible. The Cortex XDR agent uses targeted threat prevention signatures to block exploits with minimal performance impact. Currently available in private preview.
- Next-Gen Firewall Protection Visibility and Gap Analysis: See which vulnerabilities are already protected by your Palo Alto Networks firewalls, identify gaps in coverage, and get recommendations to strengthen defenses.
- Fix-Oriented Vulnerability Policies: Simplify remediation by grouping vulnerabilities that share the same fix into a single actionable issue, reducing ticket volume and accelerating resolution.
- Advanced Network Scanning Details: Gain deeper visibility into scanning activity, host behavior, and credential usage to better understand your exposure landscape.
Find More Threats With Unified Intelligence
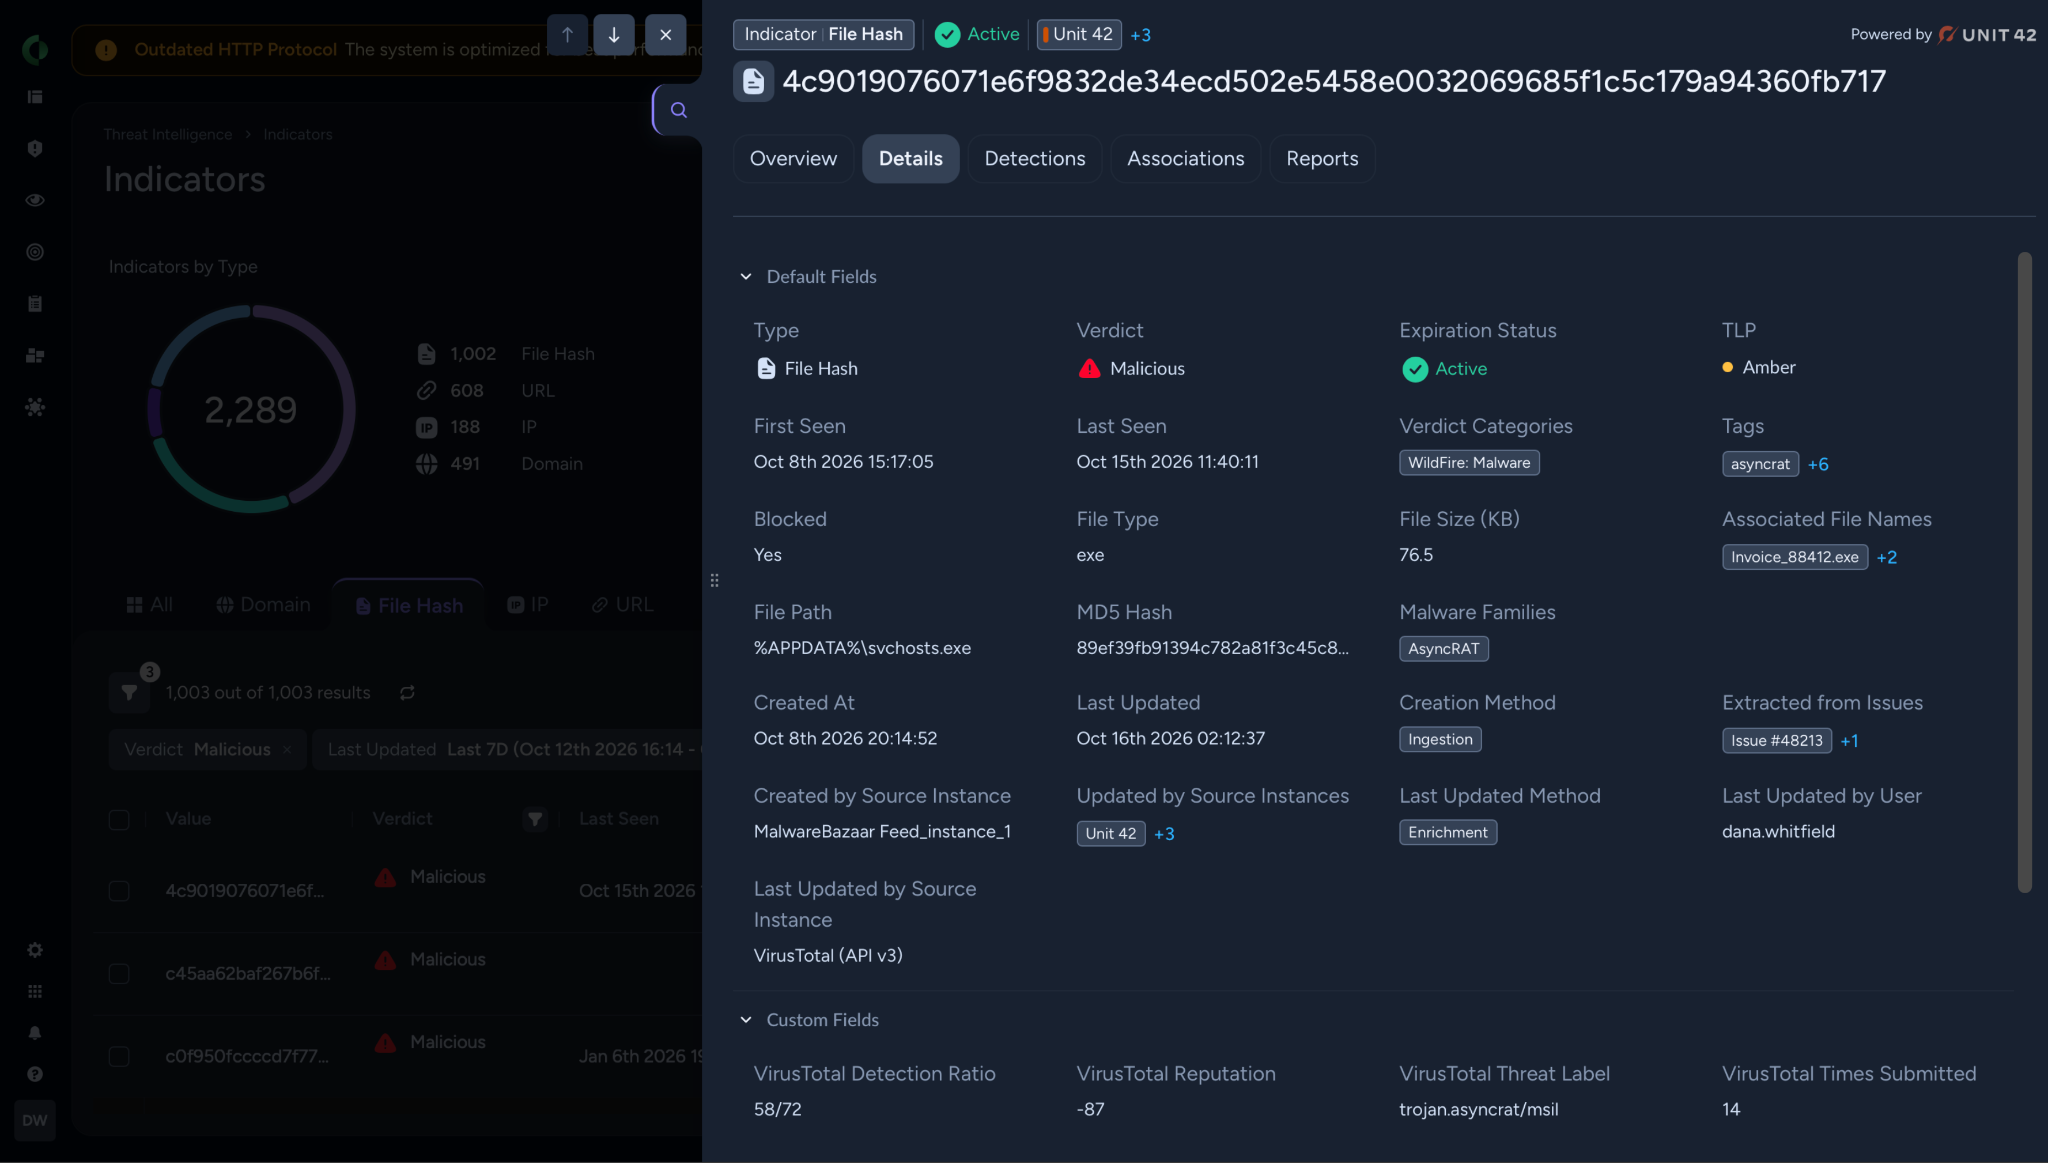
Cortex Extended Threat Intelligence (XTI) now integrates Unit 42 intelligence with third-party threat feeds, giving analysts a broader view of emerging threats. An enhanced Threat Intelligence AI agent brings deeper context into investigations, while new retrohunting capabilities search historical data to uncover previously hidden threats. With richer intelligence at their fingertips, security teams can hunt down and respond faster to advanced threats.
See the Agentic SOC in Action
Security operations is entering an era of unprecedented change. With Cortex XSIAM 4.0, we're moving closer to a world where AI handles more of the operational burden, freeing analysts to focus on the decisions that matter most.
Experience the future of security operations firsthand. Request a demo to discover how Cortex XSIAM brings AI-powered detection, investigation, and response together to accelerate your journey toward an autonomous SOC.